A new project rarely starts in a server room these days. Most teams open a cloud console, spin up a container cluster, push code through an automated pipeline, and ship it the same week. That shift, which builds on more than a decade of cloud computing model progress, is what people mean when they talk about cloud-native application development.
The numbers back this up. According to the CNCF Annual Cloud Native Survey, 59% of organizations say that much or nearly all of their development and deployment is now cloud native. Gartner separately predicts that 95% of new digital workloads will use cloud-native platforms, and for many enterprises, this shift sits at the core of their broader digital transformation programs.
This article explains what cloud-native really means in 2026, why businesses keep moving to it, which technologies make it work, and where the hidden costs and risks hide.
What Is Cloud-Native Application Development?
Cloud-native application development is a way of building software that assumes the cloud from day one rather than treating it as a hosting destination added later. Cloud-native development focuses on small, independently deployable services, automation, and infrastructure delivered through code. The cloud-native approach is shaped by a few core ideas: applications run as small, independently deployable services; infrastructure is treated as code; deployments happen many times a day; and the underlying operating system, hardware, and scaling are abstracted away through containers and managed cloud services.
How cloud-native applications differ from traditional applications
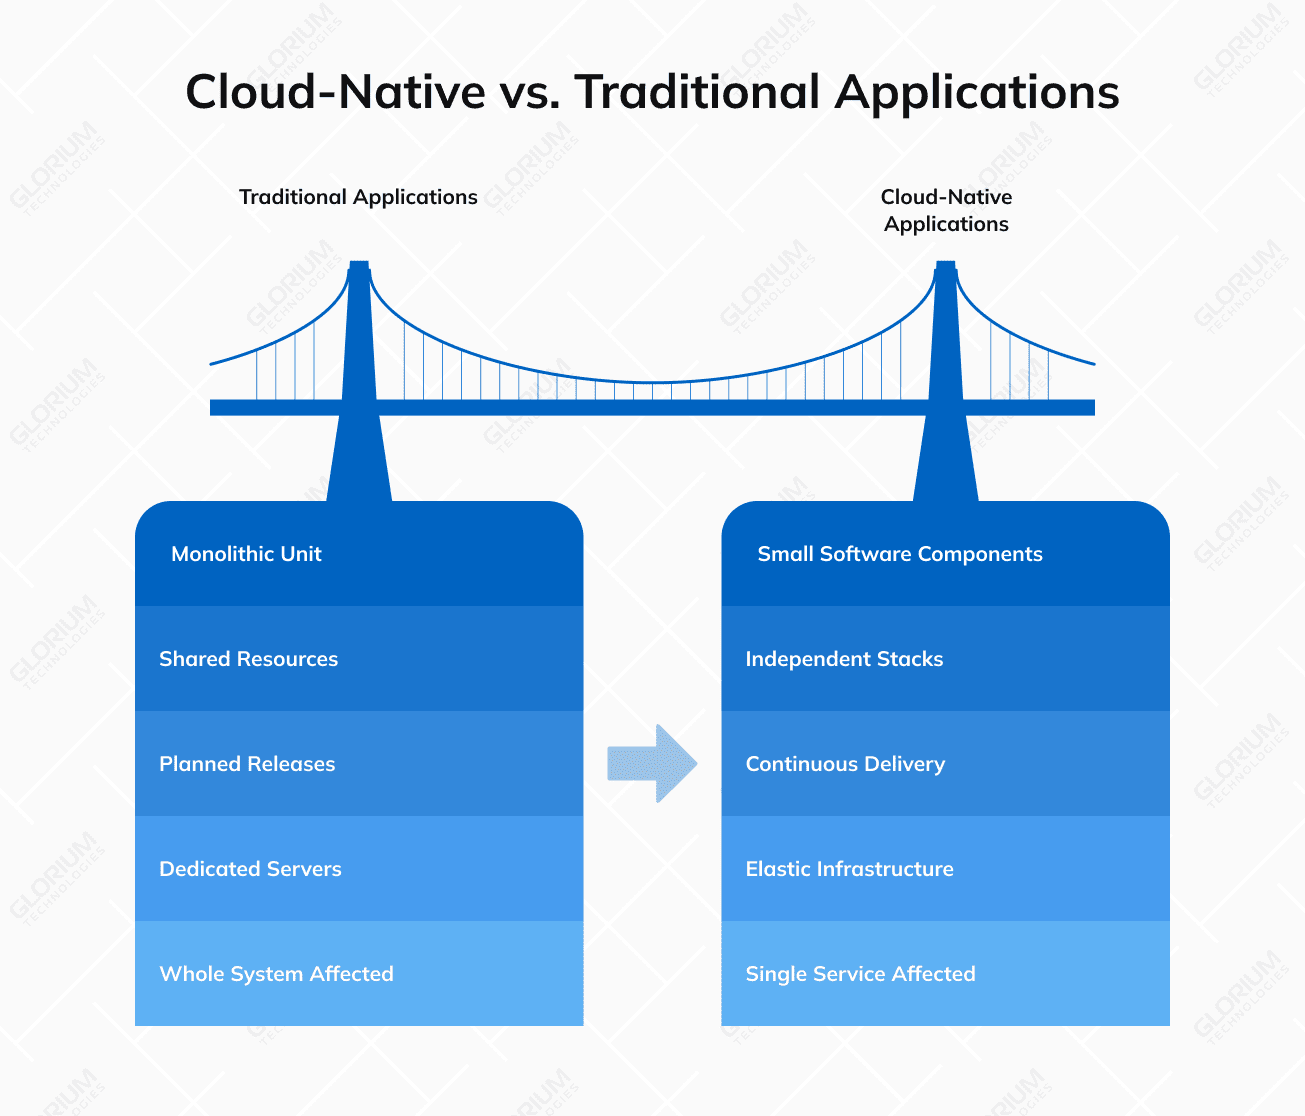
Traditional applications were usually built as a single deployable unit running on dedicated servers, with releases planned weeks in advance. Existing applications of this kind often share a database and memory, and must be tested as a whole before any change can go out.
Cloud-native applications are built differently. They are composed of small software components that talk to each other through APIs, run inside containers, and can be deployed independently. Each piece has its own technology stack, process, and release cycle. The underlying infrastructure is elastic: when traffic rises, more container instances start automatically; when it drops, those instances shut down.
This structure changes how teams work. Development and operations teams plan around continuous delivery instead of big-bang releases. If something breaks, only one service is affected rather than the entire product.
The cloud-native development model in practice
In a typical cloud-native app development workflow, code lives in a version control system, automated tests run on every commit, container images are built and stored in a registry, and a deployment pipeline pushes those images to a Kubernetes cluster or a serverless runtime. Automation runs through the entire software development lifecycle, from commit to production. Observability tools collect logs, metrics, and traces from every service. Security checks happen inside the same pipeline, not after the fact.
Wondering how this looks on a real project? In a secure cloud migration for a media company, our team rebuilt a content platform on Google Cloud Platform using Kubernetes for orchestration and Jenkins for CI/CD. The work involved containerizing legacy services, splitting tightly coupled components into microservices, and putting observability in place before turning off the old environment. The result was a system that could absorb traffic spikes without manual intervention, and ship updates daily instead of monthly.
Why Businesses Are Adopting Cloud-Native Development in 2026
The case for a cloud-native platform is no longer theoretical. It rests on three measurable outcomes: faster software delivery processes, better resilience under load, and more predictable economics when usage patterns shift. Below, we look at each in turn, with data from recent industry research.
Faster software delivery and shorter release cycles
The biggest practical reason businesses move to cloud-native software development is speed. Continuous integration and continuous delivery pipelines, combined with container orchestration, let teams ship code multiple times a day instead of every quarter. Many leaders believe their cloud platform investments are driving enterprise value, with productivity being the top measure cited.
For product-led companies, the impact shows up at the team level. Code reviews shrink, deployment processes become routine, and developers spend more time on features than on operational firefighting.
Built-in scalability and resilience
Cloud-native architecture is designed for the distributed nature of modern traffic patterns. Building scalable applications used to require careful capacity planning months in advance; today, services scale horizontally by adding more instances rather than buying a larger server. If one container fails, the orchestrator replaces it automatically. Rolling updates and rollbacks happen without downtime.
Microservices architecture is central to this. By breaking an application into smaller, loosely coupled services, teams can scale only the parts under pressure. A search service can run 50 instances during a peak hour, while the billing service runs three. Resource utilization improves significantly compared with scaling an entire monolith.
Better cost efficiency through resource utilization
Cloud services bill per minute of compute, per gigabyte of storage, and per million requests. When applications are designed to use only what they need at any moment, costs follow real demand rather than peak forecasts. Serverless computing pushes this further: code runs only when invoked, and there are no idle servers between requests.
Core Technologies Behind Cloud-Native Applications
A handful of technologies show up in nearly every cloud-native project. They cover different layers of the stack and tend to be used together rather than in isolation. The table below summarizes how each fits.
|
Technology layer |
Examples |
What it does |
Why it matters for cloud native |
|
Containers |
Docker, containerd |
Package code with its dependencies into a portable unit |
Same image runs locally, in staging, and in production |
|
Container orchestration |
Kubernetes, Amazon ECS |
Deploys, scales, and heals containers across machines |
Removes manual server management at scale |
|
Microservices architecture |
Spring Boot, FastAPI, .NET microservices |
Breaks an application into small services with their own data |
Independent deployment and scaling |
|
CI/CD |
GitHub Actions, GitLab CI, Jenkins, Argo CD |
Builds, tests, and deploys code automatically |
Enables many small releases per day |
|
Service mesh and APIs |
Istio, Linkerd, gRPC |
Manages service-to-service traffic, security, and observability |
Makes distributed systems debuggable |
|
Observability |
Prometheus, Grafana, OpenTelemetry |
Collects metrics, logs, and traces from every service |
Required to operate distributed systems safely |
|
Serverless computing |
AWS Lambda, Azure Functions, Google Cloud Run |
Runs code only when triggered, no server management |
Lowest operational overhead for event-driven workloads |
Containers and container orchestration
Containers are the building blocks of cloud-native applications. A container packages an application together with its runtime, libraries, and configuration into a single image that runs the same way anywhere. Production Kubernetes deployments reached 80% in 2024 according to the CNCF 2024 Annual Survey, and the global application container market hit $5.85 billion in 2024 with projections to reach $31.50 billion by 2030.
Kubernetes itself handles the operational side. It schedules containers across a cluster of machines, restarts failed instances, balances traffic, rolls out new versions, and rolls them back when something looks wrong. For most teams building cloud-native systems, Kubernetes is the default orchestration layer, with managed offerings from every major cloud provider.
Microservices architecture
Microservices architecture is the design pattern that makes cloud-native applications easier to evolve. Instead of one large codebase, an application is split into small services, each with a single responsibility, its own data store, and a clear API. Services communicate over HTTP, gRPC, or asynchronous message queues.
The benefits are well-documented: independent scaling, smaller blast radius when something fails, parallel work across teams, and the freedom to use different languages for different services. The cost is operational complexity, which is why microservices and Kubernetes tend to arrive together.
CI/CD and DevOps practices
Continuous integration and continuous delivery are not optional in cloud-native development. They are how code reaches production safely when releases happen daily. A typical CI/CD pipeline runs tests, builds a container image, scans it for vulnerabilities, pushes it to a registry, and triggers a deployment to a cluster, all from a single commit.
DevOps practices wrap around this. Infrastructure is defined in code using tools like Terraform or Pulumi. Configuration changes go through pull requests. Monitoring dashboards live next to the application code. The line between developers and operators thins, which is exactly the point.
Cloud-Native Architecture and Design Principles
Architecture decisions made early in a cloud-native project shape how well the system scales, how easy it is to debug, and how safely it can be changed. A few principles show up consistently in well-designed cloud-native systems.
Immutable infrastructure and declarative configuration
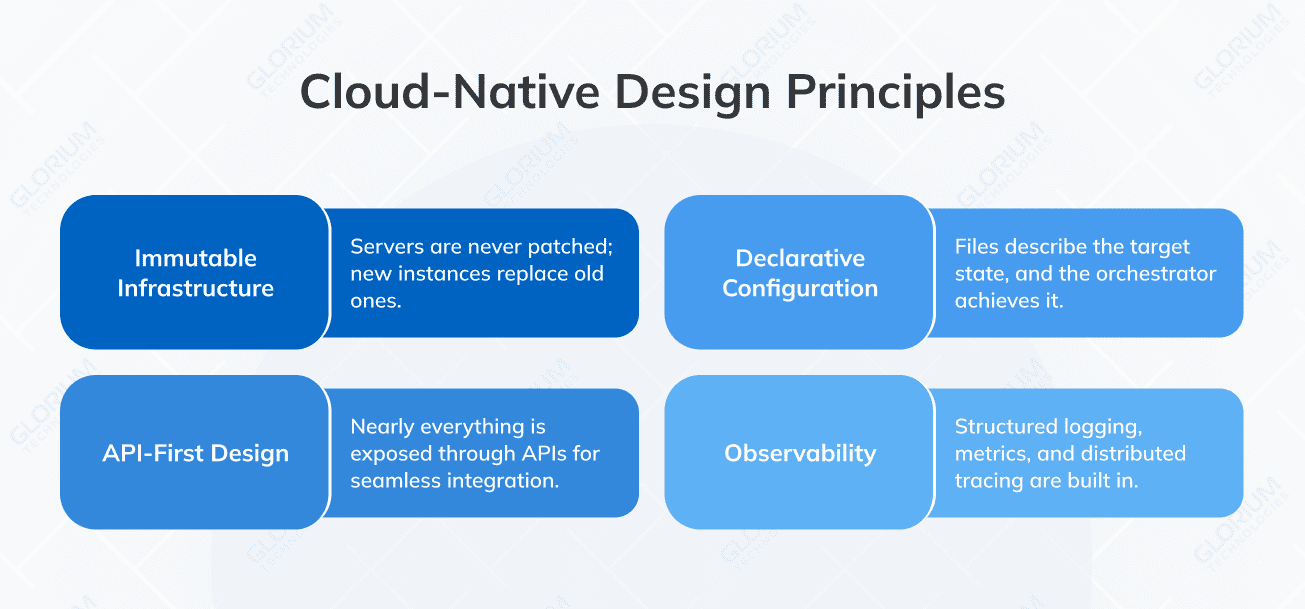
In a cloud-native model, servers are never patched in place. When something needs to change, a new container image is built, and a new instance replaces the old one. This is called immutable infrastructure, and it eliminates the long-standing problem of servers that drift away from their original configuration over time.
Declarative configuration is the companion idea. Instead of writing scripts that describe how to reach a target state, engineers write files that describe the target state itself. The orchestrator figures out how to get there. This makes cloud deployments predictable and reproducible across environments.
API-first design and seamless integration
Cloud-native applications expose nearly everything through APIs. Internal services talk to each other over APIs. External clients, including mobile apps and partner systems, integrate through APIs. The discipline of designing the API before the implementation pays off later: clear contracts make services easier to replace or extend without breaking dependent systems.
This is also why cloud-native apps integrate so well with each other. A new feature often becomes a new service, and that service simply joins the existing mesh of APIs. Seamless integration with cloud vendors and SaaS partners follows the same pattern.
Observability across distributed systems
The hardest operational problem in cloud-native systems is understanding what is happening when something goes wrong. With dozens of services running across hundreds of containers, traditional log files are not enough. Cloud-native software builds in structured logging, metrics, and distributed tracing from the start.
OpenTelemetry has become the standard framework for this. It captures the path of every request as it moves through services, which is the only practical way to debug latency or errors in a distributed system. Teams that skip observability in early development almost always regret it later.
Challenges and Risks of Cloud-Native Adoption
Gartner predicts that 25% of organizations will have experienced significant dissatisfaction with their cloud adoption by 2028 due to unrealistic expectations, suboptimal implementation, or uncontrolled costs. The challenges below are the most common in real projects.
Operational complexity and skills gaps
Cloud-native systems have a lot of moving parts. Kubernetes alone has a steep learning curve, and once a team adds service meshes, observability stacks, secrets management, and policy engines, the cognitive load on engineers grows quickly. Cultural challenges, skills gaps, and operational complexity continue to slow progress for organizations even after they have adopted the basic tools.
This is one of the reasons businesses bring in dedicated development teams with cloud-native experience rather than learning everything from scratch. The cost of an under-skilled team running production Kubernetes is usually higher than the cost of hiring experienced help.
Cost surprises and resource utilization
Cloud pricing rewards careful design and punishes carelessness. A misconfigured autoscaler, a forgotten test cluster, or an inefficient query against a managed database in a busy cloud environment can quickly add five figures to a monthly bill. Cost discipline in cloud-native projects means setting budgets, instrumenting spend per service, and reviewing utilization regularly. Tools exist for this, but the harder part is the organizational habit.
Security across the distributed nature of cloud-native systems
Containers, microservices, and APIs multiply the surface area of an application. Each service is an entry point. Each container image is a potential vulnerability if its base image is outdated. The 2025 Gartner Market Guide for Cloud-Native Application Protection Platforms estimates that half of all enterprise applications will run in containers, which is exactly why dedicated CNAPP tooling has emerged as a category.
Practical cloud-native security combines image scanning, runtime monitoring, least-privilege access management, network policies between services, and secrets management. For regulated industries, all of this has to be documented and auditable. Glorium Technologies works with HIPAA, GDPR, SOC 2, and ISO 27001 frameworks on healthcare and fintech projects where compliance is part of the architecture, not an afterthought.
Future Trends in Cloud-Native Development
Cloud-native development has matured into the default approach for new digital workloads, and the more interesting question for engineering leaders is what gets built on top of it. A few trends are already visible in 2026.
AI workloads on cloud-native platforms
The biggest shift in 2025 and 2026 has been the convergence of AI infrastructure and cloud-native platforms. The 2025 CNCF Annual Cloud Native Survey found that 66% of organizations hosting generative AI models use Kubernetes to manage some or all of their inference workloads. Kubernetes has effectively become the operating system for production AI.
This affects how new products are designed. Teams building AI-native applications typically need GPU scheduling, vector databases, model serving infrastructure, and the same CI/CD discipline as any other cloud-native app. AI software development services and cloud-native development are merging into a single discipline in many engagements.
“If you look at cloud native, the problem that cloud native was seeking to solve was really a compute and scalability problem. We basically had an initiative where businesses asked for more performance, and the cloud was a solution for it. But with AI native, we are really trying to solve a completely different set of problems: how can we get those systems we scaled using cloud to learn, to act, and to decide pretty much autonomously.”
— Ravi Balaur, Founder, Precession Partners
Hybrid clouds and sovereign cloud requirements
Regulatory pressure is reshaping where cloud-native workloads run. Gartner predicts that 90% of organizations will adopt a hybrid cloud approach through 2027. For businesses in healthcare, finance, and the public sector, data residency rules now influence which cloud provider can host which workload, and many architectures need to support multiple regions or even on-premises deployments alongside public cloud.
Cloud-native technologies handle this reasonably well. Kubernetes, containers, and CI/CD pipelines work the same way across AWS, Azure, Google Cloud, and on-premises infrastructure. Portability is one of the practical benefits of the cloud-native approach.
Platform engineering as the new normal
The third major shift is organizational. Rather than asking every product team to manage its own Kubernetes clusters and pipelines, large engineering organizations are building internal platforms that abstract those concerns. A platform engineering team owns the developer experience: paved roads for deployment, golden paths for common architectures, and self-service portals for provisioning environments. Product teams ship features. This pattern is becoming standard in companies with more than a few dozen engineers.
Start Building Cloud-Native Applications with Glorium Technologies
Glorium Technologies has more than 15 years of experience helping companies design, build, and operate production software, and cloud-native development services have been at the center of that work for the last several years. Our engineers build with Kubernetes, microservices, CI/CD, and managed cloud services every day, and we have shipped cloud-native systems for healthcare, real estate, fintech, media, and SaaS companies across the United States and Europe.
We meet clients wherever they are on the cloud-native journey. If you are extending an existing team with engineers who can plug in quickly, our staff augmentation services place vetted developers within two to four weeks. If you are building a new product from scratch, a dedicated development team gives you a stable group that owns the work end-to-end. For modernization projects, our legacy application migration practice handles the move from monolithic systems to cloud-native architectures without breaking what already works. When AI is part of the roadmap, our AI software development services plug directly into the same cloud-native foundation.
Every engagement is scoped around clear deliverables, security requirements, and performance metrics. We hold ISO 27001 certification, work under HIPAA and GDPR frameworks, and have delivered cloud-native projects under tight regulatory constraints in healthcare and finance.
If you are planning a cloud-native build, a migration, or a modernization initiative for 2026 and want to talk through scope, timeline, and budget, book a free intro call with our team. We will walk through what your specific project might look like and where the real risks and real savings sit.
FAQ
What is the difference between cloud-native and cloud-enabled applications?
Cloud-enabled applications are traditional monolithic apps rehosted on cloud infrastructure, but still running as a single deployable unit. Cloud-native applications are built from the ground up for the cloud, using containers, microservices, and managed services to take full advantage of elasticity and automated scaling.
Can we migrate a monolithic application to cloud-native gradually?
Yes, and that is usually the safer path. The strangler fig pattern is common: peel off one feature at a time into a new microservice, route traffic to it, and retire the matching piece of the monolith. Most enterprise migrations take 12 to 24 months and run alongside the legacy system throughout.
Does cloud-native development create vendor lock-in?
Less than many people assume, if the architecture stays portable. Workloads built on open standards like Kubernetes, OpenTelemetry, and Postgres run across AWS, Azure, Google Cloud, and on-premises with limited rework. Lock-in mostly comes from proprietary services like serverless functions and managed databases, which are still worth using when the productivity gain outweighs the migration risk.
When is cloud-native development the wrong choice?
Small internal tools with predictable load, short-lived prototypes, and applications with strict on-premises hardware dependencies rarely benefit from cloud-native complexity. The cost of running Kubernetes and a full observability stack is hard to justify when a single VM and a basic deployment script would do the same job.
What roles are needed on a cloud-native development team?
A typical team includes backend and frontend engineers, a DevOps or platform engineer who owns the cluster and CI/CD pipelines, an SRE for production reliability, a security engineer for compliance-sensitive projects, and a QA engineer for test automation. For smaller products, some roles can overlap, but the DevOps and security functions are hardest to skip.
About Hanna Reshetniak