HIPAA-Compliant App Development in 2026: Features, Tech Stack, AI Rules, and Cost
[vc_row][vc_column][vc_column_text]
The growing digitization of the healthcare sector brings significant opportunities but challenges, especially when protecting patient data. HIPAA, passed in 1996, sets standards for safeguarding medical information in the United States. HIPAA compliance is a non-negotiable requirement if you’re developing a healthcare mobile app.
The pressure keeps growing. In 2025, healthcare organizations reported a record 772 large data breaches to the HHS Office for Civil Rights, according to The HIPAA Journal. IBM’s 2026 Cost of a Data Breach Report puts the average healthcare breach at $6.64 million, the highest of any industry.
In this article, we will delve into HIPAA-compliant app development features, the solutions for achieving this, and the associated costs. You will also see the tech stack behind compliant builds, how AI changes your obligations, what the proposed Security Rule update means for 2026, and whether an MVP can launch before full compliance.
Industry compliance should be at the heart of any healthcare startup’s strategy. It has key rules that serve as a mandatory basis for the development of all desktop and mobile solutions. Failure to comply with these rules means that your software and/or apps will be rejected from the market.
HIPAA stands for the Health Insurance Portability and Accountability Act. This regulation of the U.S. healthcare industry was first developed in 1996. Essentially, it is a federal law mandating the development of national standards to prevent the disclosure of confidential patient health information without the patient’s consent or knowledge.
HIPAA regulates healthcare providers, clearinghouses, business associates, and health plans. Providers, plans, and clearinghouses are each a covered entity. Any company that handles protected health information on their behalf, including the team that builds and hosts your app, is a business associate, signs a business associate agreement (BAA), and carries direct liability for violations.
Each HIPAA rule turns into concrete product decisions.
|
Rule |
What it means for your app |
|
Privacy Rule |
Consent flows, minimum necessary access, patient access to medical records |
|
Security Rule |
Administrative, physical, and technical safeguards: encryption, access controls, audit controls, risk analysis |
|
Breach Notification Rule |
Incident detection and a notice workflow that meets the 60-day limit |
|
Enforcement Rule |
Penalty tiers based on culpability (see the penalties section) |
|
Omnibus Rule (2013) |
A signed BAA with every vendor and subcontractor that touches PHI |
It’s no secret that regulatory compliance is essential in healthcare, especially regarding technological advances. Given the level of privacy of medical data, any breach or noncompliance can lead to costly and embarrassing consequences for patients, healthcare software providers, and medical facilities.
HIPAA compliance is required for healthcare apps that handle PHI for a covered entity or business associate. Consumer wellness apps may fall outside HIPAA, though the FTC Health Breach Notification Rule can still apply; the FTC’s health privacy guidance for businesses explains which laws may cover your product. Hospitals and healthcare providers who fail to comply with HIPAA are subject to significant fines. Under the January 2026 schedule, a single violation can cost from $145 to $2,190,294.
HIPAA has strict rules for handling, transferring, and storing personal data. Any modern IT architecture is built on a modular basis based on microservices. It is the engineering team’s responsibility to ensure that system security standards are met during HIPAA-compliant app development.
[/vc_column_text][wgl_spacing spacer_size=”30px”][vc_column_text]
To ensure that these standards are met, it is often not enough to simply structure data streams for better information control. It is important to provide encryption of channels, secure data storage, and a multi-level authorization system. It is important to know that HIPAA compliant app development often requires more than technical implementation, including:
- Well-written privacy and security policies
- Regular training and/or certification of employees
- Rigorous security assessments of third-party partners and vendors
- On-site incident plans
 Anna VoznaAccount Executive, Glorium Technologies
Essential aspects of HIPAA-compliant app development criteria include that only authorized medical personnel should have access to patient information and records. Internal espionage is, unfortunately, a common occurrence in the healthcare industry.
The HIPAA Journal reports that unauthorized access and disclosure incidents, including staff snooping on medical records, rose again in 2025, based on OCR breach portal data. In addition to proper staff training, AI can flag unusual access, alongside strict access controls.
In practice, that means role-based access control tied to job function, multi-factor authentication for every account that can open patient records, and same-day revocation of user access when an employee leaves.
But even this is not always enough to fully protect the data. There are situations where it is not the app that is attacked but the medical system to which it is connected. In such cases, an attacker may forge a certificate to intercept traffic and gain access to the data on the server or client devices.
To ensure HIPAA compliance, your app must have clear, traceable processes for every action involving Protected Health Information (PHI). Vendors that provide mobile app development services build audit trails and safeguard data integrity from the start.
Here are the key challenges that stall the development process:
Here’s how to build and audit controls and integrity:
We recommend focusing on these technical and procedural aspects from the initial design phase. You can create a strong foundation of trust and integrity right away by making ongoing compliance audits more straightforward and less prone to costly violations.
As healthcare businesses gradually move to digital platforms, data security is becoming an increasingly important issue. Hacking and other IT incidents now cause more than 80% of large healthcare data breaches, according to The HIPAA Journal.
In 2025 alone, large breaches exposed the protected health information of roughly 138.5 million people. The accumulation of sensitive patient data, medical records, and smart data from medical wearable devices is becoming a target for devastating and costly cyberattacks and data breaches.
For a mobile app, transmission security comes down to TLS 1.2 or higher on every API call, certificate pinning against man-in-the-middle attacks, and short-lived signed tokens so an intercepted request cannot be replayed.
Whether you need to build a HIPAA-compliant app from scratch or upgrade an existing one, below is a breakdown of the core features your HIPAA-compliant mobile app needs to ship with, organized by function.
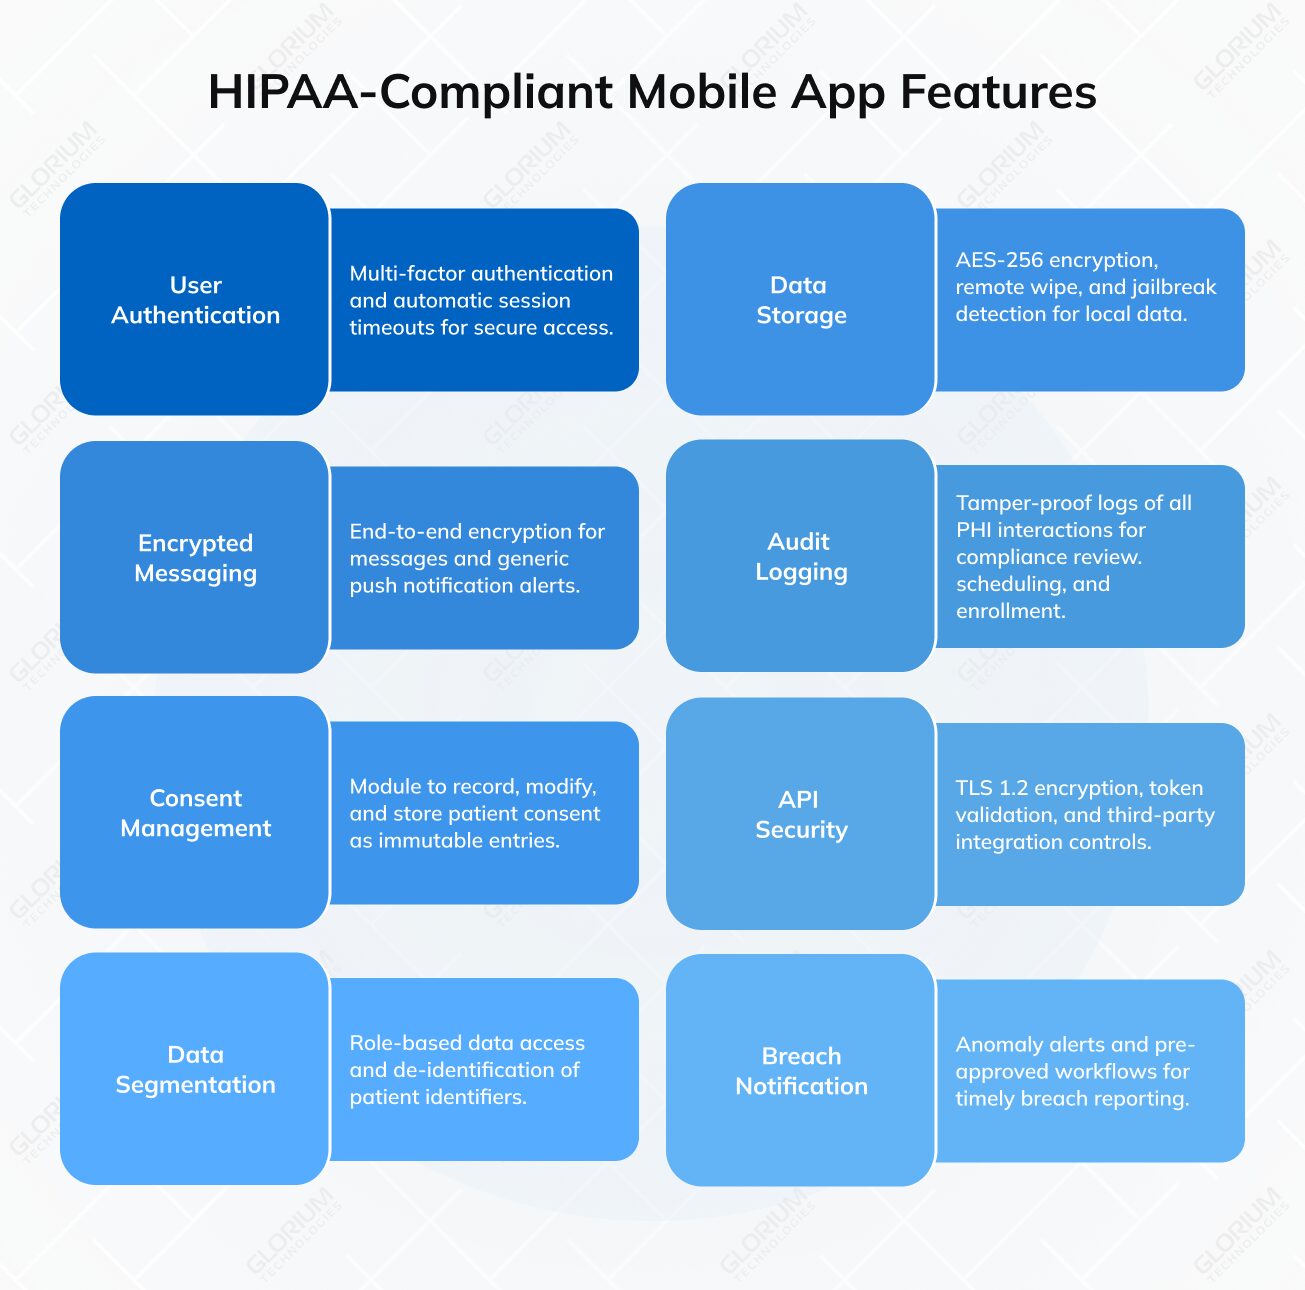
Every interaction with PHI begins at the login screen. Your app should support multi-factor authentication that combines something the user knows (password or PIN) with something they have (a hardware token or authenticator app) or something they are (fingerprint or facial recognition). Beyond login, session management matters just as much. Automatic session timeouts should lock the app after a defined period of inactivity, typically two to five minutes for clinical settings. Re-authentication should be required before any high-risk action, such as exporting records or modifying patient data.
If your app enables communication between providers, staff, or patients, every message containing PHI must be encrypted in transit and at rest. This applies to text, images, file attachments, and video. The messaging module should also prevent PHI from appearing in push notification previews on lock screens, since a notification reading “Lab results for John Smith” on an unattended phone is a compliance violation waiting to happen. Configure notifications to display generic alerts (“You have a new message”) instead.
HIPAA requires patient authorization for uses beyond treatment, payment, and operations. Build a consent management module that records exactly what the patient agreed to, when they agreed, and which version of the policy they reviewed. Allow patients to revoke or modify consent directly within the app. Store these consent records as immutable audit entries so they can be produced during a compliance review.
Not every screen or report needs to display full patient identifiers. Implement data segmentation so that different user roles see only the data elements relevant to their function. A billing coordinator does not need access to clinical notes, and a nurse may not need to see payment history. Where analytics or reporting features exist, apply de-identification methods aligned with HIPAA’s Safe Harbor standard, removing all 18 identifier types before data enters any analytics pipeline.
PHI stored locally on a mobile device introduces significant risk. If local caching is necessary for offline functionality, encrypt all local databases using AES-256 or equivalent standards. Implement remote wipe capabilities so that if a device is lost or stolen, an administrator can erase stored PHI. The app should also detect jailbroken or rooted devices at launch and restrict access, since these devices lack the OS-level security controls your encryption depends on.
Every interaction with PHI should generate a log entry: who accessed the data, what they viewed or modified, from which device, and at what time. These logs must be tamper-proof and retained according to your organization’s data retention policy (HIPAA requires a minimum of six years for certain documentation). Any team focused on HIPAA-compliant software development should build a dashboard or export function so compliance officers can review activity without needing engineering support.
Mobile apps rarely operate in isolation. They connect to EHR systems, lab platforms, payment processors, and cloud storage. Every API endpoint handling PHI must enforce TLS 1.2 or higher, validate authentication tokens on each request, and rate-limit calls to prevent brute-force attacks. When integrating third-party services, verify that each vendor has signed a Business Associate Agreement and that their specific services are HIPAA-eligible. Not every product tier from a cloud provider qualifies, so confirm eligibility at the service level, not just the vendor level.
The breach notification rule allows no more than 60 days after discovery to notify affected individuals. Breaches affecting 500 or more people must be reported to HHS within 60 days, and to the media when more than 500 residents of a state are affected. Smaller breaches are reported to HHS once a year. Anomaly alerts on top of audit logging, plus a pre-approved notice workflow, let your team respond without improvising.
Building these features into your architecture from day one is far less expensive than retrofitting them after launch. Each one addresses a specific HIPAA safeguard requirement, and together they form the technical backbone of a compliant mobile application.
No framework or cloud makes an app compliant by itself; configuration and BAA coverage decide that. Here is a proven stack for HIPAA-regulated builds.
|
Layer |
Technologies |
HIPAA role |
|
Mobile |
Swift, Kotlin, React Native, Flutter |
Keychain/Keystore credential storage, biometrics, certificate pinning |
|
Back end |
Node.js, Python (Django, FastAPI), .NET, Java (Spring Boot) |
Server-side role-based access control, input validation, rate limiting |
|
Databases |
PostgreSQL, Amazon RDS, Azure SQL, MongoDB Atlas |
Encryption at rest, field-level encryption, automated backups |
|
Cloud |
AWS, Microsoft Azure, Google Cloud (BAA-covered services only), AWS KMS |
HIPAA-compliant infrastructure, network isolation, key management |
|
Identity |
OAuth 2.0, OpenID Connect, Auth0 or Okta (BAA tiers), Amazon Cognito |
Multi-factor authentication, single sign-on |
|
Communication |
Twilio HIPAA-eligible services, WebRTC over TLS |
Secure messaging and video visits |
|
Interoperability |
HL7, Fast Healthcare Interoperability Resources (FHIR), SMART on FHIR, DICOM |
Secure data exchange with electronic health records |
|
Monitoring and testing |
AWS CloudTrail, Datadog, Splunk, SonarQube, Snyk |
Audit trails, ongoing monitoring, security testing in CI/CD |
A BAA covers only the services named in it, so confirm eligibility service by service, and keep PHI in a store separate from analytics data. Our HL7 and FHIR integration work follows the same principle.
HIPAA-compliant app development involves a thorough understanding of the regulatory framework and implementing stringent security measures. Here is a step-by-step guide to developing a HIPAA-compliant healthcare app.
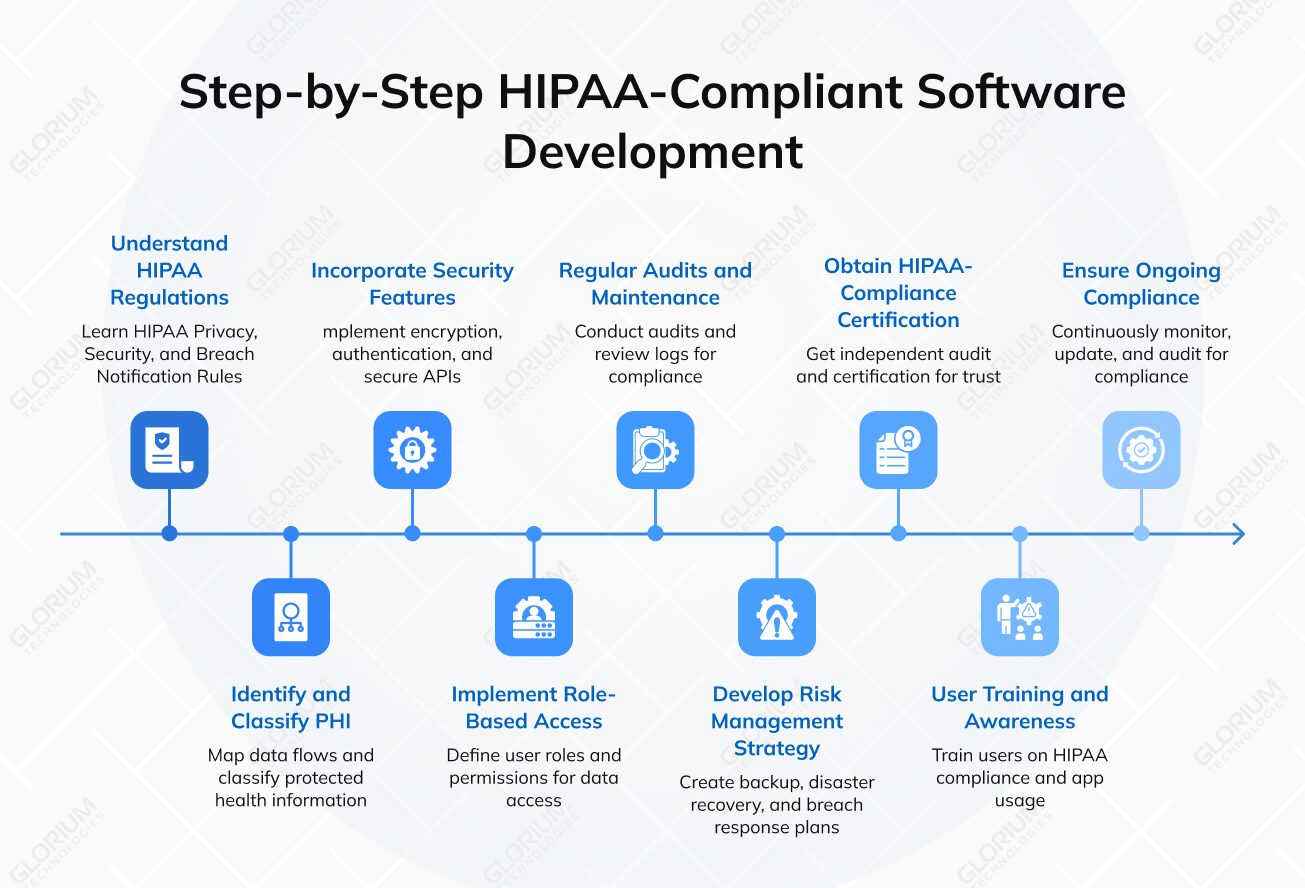
step1
The first step is understanding what HIPAA covers and how it applies to mobile apps. This includes understanding the Privacy, Security, and Breach Notification Rules. For example, you should understand the types of protected health information (PHI), what constitutes a violation, and what penalties might be involved. If you’re unsure, consulting with a HIPAA expert can help.
step2
Your app will need to identify and classify any PHI that it handles. This includes any information that can be used to identify an individual related to their health status, care, or payment for care. Map your data flows too: where PHI enters, where it rests, and which third-party vendors can see it.
step3
At its core, HIPAA is about security. HIPAA-compliant apps need robust security measures, including encryption, user authentication, automatic log-off, and secure APIs. The app should ensure secure transmission, storage, and disposal of PHI. Additionally, the app should include an emergency access procedure to ensure PHI is accessible during a crisis.
step4
Role-based access ensures that only authorized individuals have access to sensitive data. This means implementing user roles and permissions, and ensuring that each user can only access the information necessary for their job.
step5
Regular audits help to identify potential HIPAA violations and maintain compliance. It would help if you considered logging all access to PHI and regularly reviewing these logs for any discrepancies.
step6
In case of a breach, a strategy should be in place for managing the risk and minimizing the impact. This should include regular data backups, a disaster recovery plan, and a data breach response protocol.
step7
HHS does not certify apps. An independent assessment, such as a penetration test, SOC 2 Type II, or HITRUST, shows buyers that your application has gone through stringent compliance checks.
step8
Training and awareness are an integral part of HIPAA compliance. Your users, especially healthcare professionals, should understand how to use the app in a way that maintains HIPAA compliance.
step9
Compliance is not a one-time thing but a continuous process. Changes in technology, regulations, or how your app works may require changes in your compliance strategy. Regular audits, updates, and training can ensure ongoing HIPAA compliance.
The requirements are the same for every product, but the shipped version changes with what the app does.
Compliant RPM apps pair only with registered devices, encrypt readings before upload, keep offline data in an encrypted local store, and log every clinician view. Our mobile app for physiological monitoring and biofeedback connects to sensors over BLE for biofeedback, heart rate variability, and electromyography, and turns the readings into evaluation reports.
Compliant portals verify identity at sign-up, send generic notifications instead of results, and log every download; video visits run over encrypted WebRTC through a vendor that signs a BAA. Glorium Technologies built a web portal for remote fertility testing, where at-home test data has to reach patients and clinicians securely.
DICOM files carry patient identifiers in their metadata, so production systems strip them before analytics or 3D processing and serve images through short-lived signed URLs. See our project for converting medical imaging into 3D models.
HIPAA has no exception for AI. When a model, prompt, or vector database receives protected health information, the Privacy and Security Rules apply in full, and the AI vendor becomes a business associate. At the 2026 National HIPAA Summit, OCR named data leakage, data poisoning, and PHI exposure without a BAA among the main AI risks, according to Morgan Lewis.
Staff pasting records into consumer chatbots is the quieter risk, so name approved tools in your policy. Glorium Technologies builds AI solutions for healthcare with these controls from day one.
HHS proposed an overhaul of the Security Rule on January 6, 2025. The proposal is still not final: the May 2026 target passed, and the federal agenda now lists July 2027, according to The HIPAA Journal. HHS confirms the current rule remains in effect. Building to the proposal now still saves rework later.
|
Area |
Current rule |
Proposed update (not final) |
|
Encryption |
Addressable |
Required at rest and in transit |
|
Multi factor authentication |
Not explicitly required |
Required for access to ePHI |
|
Asset inventory and network map |
Not required |
Reviewed every 12 months |
|
Vulnerability scans and pen tests |
No set frequency |
Every 6 and 12 months |
|
Recovery |
Contingency plan |
Restore critical systems within 72 hours |
|
Business associates |
BAA with assurances |
Annual written verification of safeguards |
If finalized as proposed, most organizations would have 240 days after publication to comply.
Sometimes, HIPAA compliance fails in less obvious areas—oversights in process, partnership, and human factors that can quietly introduce risk. Even a technically sound HIPAA-compliant application can fall out of compliance if these foundational elements are missed:
Penalties scale with culpability. These are the official amounts from the January 28, 2026 Federal Register notice:
|
Tier |
Level of culpability |
Per violation |
Annual cap |
|
1 |
Did not know |
$145 to $73,011 |
$2,190,294 |
|
2 |
Reasonable cause |
$1,461 to $73,011 |
$2,190,294 |
|
3 |
Willful neglect, corrected in 30 days |
$14,602 to $73,011 |
$2,190,294 |
|
4 |
Willful neglect, not corrected |
$73,011 to $2,190,294 |
$2,190,294 |
Caps apply per violation type, and lower caps apply to tiers 1 to 3 in practice under OCR’s 2019 enforcement discretion, as The HIPAA Journal explains. Intentional misuse of PHI can also bring criminal fines up to $250,000 and up to 10 years in prison.
Fines are only part of the bill: IBM puts the average healthcare breach at $6.64 million once detection, notification, and lost business are counted.
Only while it runs on synthetic or de-identified data with no link to a provider or health plan. Once real PHI enters the system, even from one pilot clinic, HIPAA applies in full, with the same penalties as a mature product.
|
Must ship in the MVP |
Can wait for later releases |
|
Encryption in transit and at rest |
Advanced anomaly detection dashboards |
|
Role-based access control and MFA |
Granular consent options for secondary uses |
|
Audit logging of every PHI access |
Self-service compliance reports |
|
BAAs with cloud, messaging, and email vendors |
SOC 2 Type II report or HITRUST certification |
Retrofitting these controls later means reworking the data model, authentication, and logging. A discovery phase is the right moment to decide which data your MVP will touch.
You won’t be able to comply with all the necessary HIPAA regulations without the help of a professional developer unless you have the proper experience. As a result, working with an experienced software vendor who can help you with essential consultations and system audits is preferable.
Finding a reliable partner for HIPAA-compliant software development is vital to ensuring the success and legality of your healthcare app. Here are the steps you should follow to select the right partner:
[/vc_column_text][/vc_column][/vc_row]Eliminating risk for your company and customers is a priority that cannot be compromised. Learn more about our healthcare software development solutions today.
Many elements, including product complexity, development duration, technology set, team size, development speed, and more, determine the total cost.
Most HIPAA-compliant mobile apps cost $50,000 to $300,000 and take 3 to 18 months. This cost includes building the entire system, which must meet physical and technical security requirements. Besides, developers will also need to vet the system and pass independent security testing.
|
Complexity |
Timeline |
Cost |
Examples |
|
Basic |
3 to 6 months |
$50,000 to $100,000 |
Medication reminders, provider-linked trackers |
|
Mid-level |
6 to 12 months |
$100,000 to $200,000 |
Telehealth apps, patient portals |
|
Advanced |
12 to 18 months |
$200,000 to $300,000+ |
Remote patient monitoring, AI, EHR-integrated platforms |
Instead of developing a HIPAA-compliant mobile app from scratch, developers can use HIPAA-compliant infrastructure and solutions. However, when working with third-party vendors, it’s up to you to ensure they’re reliable when storing and processing PHI.
Compliance decisions made in the first weeks of a project shape everything after them: the data model, the vendors you sign, and how quickly you can add features like AI later. The development partner you choose therefore matters as much as the stack, because that team turns HIPAA requirements into architecture.
Glorium Technologies, with our extensive experience and specialized skills in healthcare development, can be your trusted partner in HIPAA-compliant mobile app development. For more than 15 years, we have built software for regulated industries, with deep specialization in healthcare and real estate, and Techreviewer.co named us among the top 100 medical software development companies for 2025. Here’s how we can assist you:
Choosing Glorium Technologies as your development partner means choosing a team that understands the nuances of healthcare, the importance of HIPAA compliance, and the value of a well-designed app. Ready to build HIPAA compliance features in your digital health solutions? Let’s have a quick chat. Request your free intro call with Glorium Technologies.
Yes, whenever PHI can reach them. A notification naming a lab result, or an analytics event from a condition-specific screen, sends PHI to that vendor. Sign a BAA with a HIPAA-eligible service or design those flows to carry no PHI. During discovery, Glorium Technologies maps which SDKs and notification payloads could carry PHI, so the fix lands before launch.
HIPAA does not ban offshore storage or development, but your BAA, risk analysis, and controls must cover those locations. Some health systems require U.S.-only hosting by contract, so confirm before you pick a cloud region. Glorium Technologies sets hosting regions and data residency during discovery, before any PHI reaches your infrastructure.
The current rule requires periodic updates without a fixed schedule. Plan for at least once a year and after every major change, such as a new integration or AI feature; the proposed update would make the 12-month cycle mandatory. Glorium Technologies can run a gap assessment against both the current rule and the proposal whenever your app changes.