The healthcare industry is one of the most regulated environments. It deals with humanity's most sensitive data. Daily, health-care providers and health plans handle a vast array of documents, clinical notes, lab results, insurance claims, billing details, and more. This protected health information (PHI) is the core of patient care and the modern health-care system, but it's also a prime target for fraud and breaches.
This is the critical "why" behind the HIPAA Privacy Rule. The industry doesn't see it as bureaucracy, but as a necessary framework that protects patients and your organization. Understanding such complex details is the foundation of all modern healthcare operations. In this article, we'll explore what HIPAA is, why it's necessary, and how to achieve true compliance with the help of a professional partner like Glorium Technologies.
What is HIPAA?
HIPAA (the Health Insurance Portability and Accountability Act) is the primary U.S. law that sets national standards for protecting sensitive patient health information.
The core purpose of this act is to protect an individual's health information. It gives patients rights over their own health data while requiring organizations to handle the data with strict safeguards in place.
HIPAA applies to:
- Healthcare providers: doctors, clinics, hospitals, psychologists, dentists, nursing homes, and pharmacies
- Health plans: Health insurance companies, HMOs, employer-sponsored group health plans, and government programs like Medicare and Medicaid
- Health-care clearinghouses: Entities that process non-standard health information into a standard format (or vice versa)
- Business associates: Third-party vendors or contractors who access, store, or process protected health information while performing services for a covered entity
What HIPAA protects:
- Identifiable information: Any health data that can be linked to a specific individual
- Scope of data: Relates to an individual’s past, present, or future physical or mental health, the healthcare provided to them, or the payment for that care
- Common Examples:
Medical records, diagnoses, and treatment plans
Billing information and insurance claims
Lab test results and prescription records
Conversations between doctors and patients about care
Any unique identifying information (like name, birth date, Social Security Number, or medical record number) when linked to health data
HIPAA rules ultimately ensure that every piece of individually identifiable health information is handled with the utmost care, whether it pertains to treatment, billing, or health insurance coverage.
Privacy Compliance
Now that we understand what HIPAA is, let's explore what is considered confidential information and how a healthcare system can avoid HIPAA violations.
Here are two types of confidential information protected by the security rule:
- Protected Health Information (PHI), which refers to any information about a patient’s identity
- Electronic Protected Health Information (ePHI)
We can divide the ePHI into several clusters. But only part of them corresponds to the convalescent's identity. These clusters may also comprise staff details since they can define a client's identity indirectly:
- Names of patients and facility staff providing treatment
- Anthropometric measure (height, weight)
- Residence, e-mail, IP, zip code
- Date of birth/death, visits to a doctor, hospital admission/discharge
- Telephone numbers
- Social security numbers, insurance cards, medical cards, bank accounts, licenses or certificates, etc. Any serial private document should be restricted
- Photos, even without the face. This category comprises all images of any part of the body
- Device and vehicle IDs. These refer to serial numbers, license plates, etc
- Biometric identity data. Fingerprints, retinal scans, voice recordings
- Health status details, causes for seeking aid, diagnosis, and healing steps
Recently, several provisions have been appended to the initial to include more scenarios and adapt it to digital advancements. These modifications are not exhaustive. Yet, we speak about a widespread idea that the info should be confined from disclosure. If so, an individual or body in charge shall be deemed guilty.
Three Basic Rulings of the HIPAA Privacy Rule
HIPAA stipulates several rulings for sharing private information among users, healthcare providers, pharmacies, employers, aid seekers, and others. Let's take a closer look at the three basic rulings:
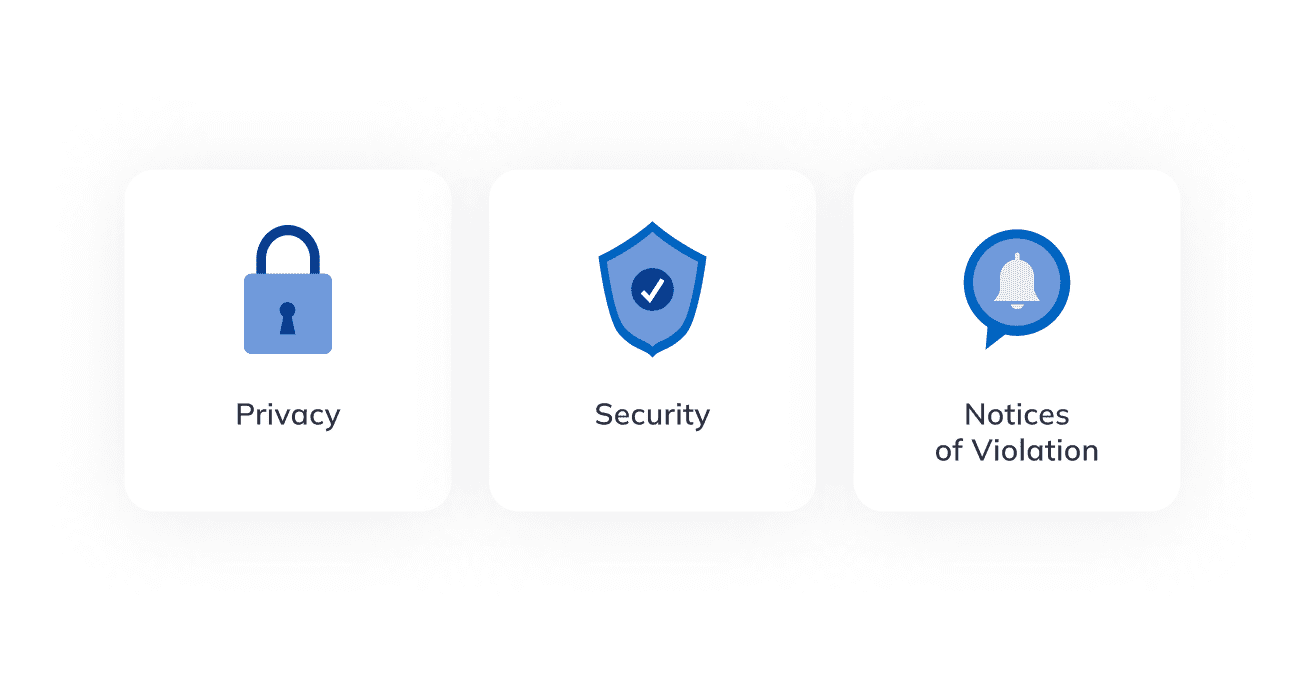
- Privacy: Principles for keeping medical files, including restrictions on when the PHI may be divulged and then used
- Security: Principles required to guarantee the confidentiality, integrity, and availability of digital PHI (ePHI)
- Notices of violation: Reporting any violations from facilities and their associates
Actors and their interaction
These regulations refer to insured bodies and respective associates. An actor is any facility that allots PHI or personal health records (PHR):
- Insurance offices;
- Healthcare providers;
- Other enterprises that manage restricted records.
A business partner may comprise any person or entity involved in providing services to insured bodies. That’s why they need the PHI. Let’s list some of them:
- Claim management and supervision;
- Data analysis, running, and storing;
- Financial or legal assistance.
An actor should conclude an agreement to offer services as a business partner. Such an agreement shall mention the allowed extent for PHI divulgence and handling. Occasionally, it gives the right to force facilities and associates to:
- Employ, claim, and divulge the minimally demanded private data.
- Implement safety actions to safeguard the PHI.
- Stick to common principles when processing certain e-transactions.
- Notify people if their PHI has been compromised.
Mostly, an agency relationship with an insured body requires a similar partnership agreement, owing to the data being divulged.
Grounds to Disclose Personal Records
Such data can be handed in certain events. If so, the person must grant a written permit to the data carrier as an actor. Each medical institution that divulges such data through digital media has to obey the Valid Confidentiality Rule. Accordingly, such data can be reported if 2 particular circumstances are met:
- Upon request. This involves the convalescent's tutor or legal representative.
- During investigations and criminal lawsuits. State Health and Human Services (HHS) are in charge of such events.
We can list several exceptions to such disclosure:
- Patient's request.
- Treatment, payment, health insurance assessment, legal assistance, and disease prognosis.
- Emergency situations, if the convalescent is unable to grant his or her permission. If so, the doctor, clinic, or insurer can decide in the patient's advantage.
- In the case of abuse, such info may be handed to authorities.
- When dealing with legal and executive proceedings.
- When identifying suspects in crimes, runaways, witnesses, or missing ones.
- When such details are deemed as evidence of a crime.
This is not an exhaustive list of exceptions. The Privacy Rule involves plenty of other stuff that allows private files to be applied with kind intentions.
The Significance for Consumers and Facilities
The benefits of HIPAA are indeed vital. This legal regulation has facilitated the switch from paper to digital carriers. Administrative functions have been simplified, productivity has increased, and management has been modernized and improved. Above all, now we can secure a safe exchange of personal papers. All enterprises with HIPAA added into their system are required to apply a set of codes and IDs. They are nationally acknowledged.
Info and transaction recording principles simplify sharing between carriers and other bodies. HIPAA adoption can yield more than simply advantages. It may be a solid shelter against major losses for businessmen.
- PHI Loss Protection. Losing sensitive particulars is a severe crime. However, we have a secure method. When using it, every employee gets a better idea of how to keep PHI safe and secret. If you obey these guidelines, HIPAA serves as a reliable dynamic defense for you and your employees from litigation.
- Interaction with the customer. HIPAA compliance allows one to learn and discover the best way to handle private files. Hiring experts to train your workforce and explain all HIPAA solutions is an excellent path to reach it.
- Increasing physical safety in the workspace. HIPAA asks entities to pay much attention to their infrastructure safety: the way they store servers, PCs, and sensitive data. Additional safety proceedings include surveillance cameras, alarm systems, etc. Only those with a certain authorization level can access sensitive info.
- Reducing checkup errors in loaded networks. Healthcare providers and patients must work together when creating medical papers because of HIPAA. As there are certain parties involved, this lowered discrepancies and possible errors in medicine. This remedy improves the overall level of attendance because the medical staff is confident in the info quality. Electronic health record (EHR) updates cleared the way for immediate examinations after introductory visits. The joined outcome of these factors has expanded the productivity lacking before.
- Loyalty. Gaining patient/customer loyalty is the core benefit. When someone can trust your institution, he or she will keep asking for your assistance.
- Regular inspections. HIPAA requires insured institutions and their partners to have inspections. Such audits uncover gaps and vulnerabilities within an organization. Without these audits, many facilities could not tell how or why their infrastructure was compromised. Therefore, HIPAA forces them to find suitable ways to assess and address gaps in security and data retention policies.
- Setting up differentiation to speed up competitiveness. HIPAA compliance is not binding. Many companies would rather avoid it to save money and cut costs. However, by doing so, you may not only face huge penalties and lawsuits but also smear your reputation. It sets you apart from your rivals and gains loyalty. This is a low-cost way to foster your company's reputation and stand out from other industry partners.
- Lower liability. Sticking to these laws, your entity can secure your patients' files, keep them safe, and avoid leaks. Thereby, you will bypass heavy fines.
- Increased cybersecurity. Yet another benefit entails those institutions must keep their databases, networks, and software up-to-date. Streamlined and modern hardware automatically reduces the error incidence. You must be far more aware of malware that might compromise customer privacy. Many documents have been hacked due to improper cybersecurity measures.
Compliance Requirements
The Health Insurance, Portability and Accountability Act bases on the cybersecurity foundation of the NIST. They insist on the enforcement of physical, regulatory, and high-tech enactments. This may keep PHI private and consistent. It may protect from unauthorized use and damage. This regulation commits affected entities and partners to:
- Ensure confidentiality, unity, and attainability of every digital PHI produced, obtained, stored, and disseminated.
- Catch and prevent any warnings.
- Shield against expected misuse or divulgence.
- Warrant that all the staff and representatives adhere to these rules.
This practice requires everyone involved to investigate and handle any breach or other incident with potential unauthorized access, use, or divulgence. Barring some restricted situations, any unauthorized access to a data subject's PHI makes up a leak. The key to securing devices from the very beginning is to consider specific cybersecurity menaces as part of the design and development affair. Manufacturers should incorporate these practices into their medical device design processes to safely maintain and decommission medical devices.
Software Solutions
Building HIPAA-compliant software is an extremely tough task. That's why it's worth relying on companies that already offer out-of-the-box solutions. Our experienced crew shows the best way to get your solution compliant for you to avoid fines and sanctions. HIPAA compliance software development offers advanced aspects to collect and manage sensitive info.
This directive requires deploying certain initiatives on every level to ensure the safe ingress, servicing, and retrieval of the PHI. While considering respective menaces and pitfalls, medical facilities should address three major questions:
- Can the source of ePHI and PHI be identified internally, involving those produced, obtained, serviced, or divulged?
- Are there external sources?
- Are there any challenges to info infrastructures?
Addressing these questions helps define the steps needed to support or evolve a compliant and safe managerial workflow. Here it is:
- Institute a staff selection policy;
- Designate the info to be backed up;
- Ways to create backups;
- Ways to apply ciphering;
- Info to be authenticated;
- Login management tool.
Enterprises can lower the exposure to supervisory intervention via special education classes. OCR suggests the respective guidance. Several counseling and instructional groups also feature such classes.
Compliant Solutions
Healthcare software development is a vital issue for organizations handling sensitive info. We have no formal compliance assessment efforts in place. Instead, we may find compatible supplements to balance patient safety with advances in MedTech. This could be a cross-platform mobile or web-based application to integrate patient/physician interaction. To do this, you need to find a balance between speed and compatibility. This involves native features, HealthKit/GoogleHealth integrations, live chat, etc. The app must drive and analyze large-scale info, which is useful for clinics. This will allow it to integrate with the EHR.
- Computer monitoring program. It traces all user actions performed, along with monitoring the server. It enables you to solve security incidents in real-time.
- DLP System (Data Leak Prevention). It protects the network; effectively blocks any actions if we speak about an info capture attempt. It regards both theft and accidental leaks.
The HHS Office has created the ultimate guide consisting of 7 particulars. These are basic, bare minimum expectations that the software must meet:
- Introducing in-word policies, practices, and ethics-related codes.
- Appointing a person and board in charge of audits.
- Implementing effective educational courses.
- Promoting viable communicative channels.
- Undertaking in-house inspections and audits.
- Upholding standards via a widely advertised disciplinary policy.
- Taking swift steps to handle violations and addressing them.
When the OCR is conducting an inquiry regarding certain breaches, investigators shall match your compliance policy to these 7 items to evaluate its impact.
The lengthy directory of requirements that are modified and amended routinely, coupled with major fines, merely underscores the importance of HIPAA-compliant app development to protect healthcare data. If you're committed to making your solution as such, get in touch with us. Our experts can assist you in your task. From a thorough review of your idea and comprehensive consultation to a full-scale, impactful compliance procedure. We'll do the complete job.
FAQ
What are the 5 main rules of HIPAA?
The five core rules of HIPAA are: the Privacy Rule (regulating the use of protected health information), the Security Rule (safeguarding electronic data), the Breach Notification Rule (mandating the reporting of breaches), the Enforcement Rule (outlining penalties), and the Omnibus Rule (updating compliance requirements for business associates).
What are the three main goals of HIPAA?
HIPAA's primary goals are: to ensure the privacy and security of patient health information, to streamline industry operations and reduce costs, and to guarantee health insurance coverage portability and continuity (often referred to as the health insurance reform act provisions).
Are small healthcare practices exempt from HIPAA?
No. HIPAA applies to any healthcare provider that transmits health information electronically in connection with a standard transaction.
What is the most common HIPAA violation?
The most common HIPAA violation is the unauthorized access, use, or disclosure of protected health information. In practice, this may look like employees snooping in patient records without a job-related need or inadvertently sharing information with the wrong person.
How often do employees need HIPAA training?
HIPAA requires that all employees receive training upon hiring and regularly thereafter. While the law doesn't specify an exact annual deadline, annual refresher training is the standard, industry-wide best practice for maintaining compliance.
What is considered a HIPAA violation?
A HIPAA violation is any failure to comply with its rules, including the improper use or disclosure of how protected health information is handled. This can range from a lost laptop to a failure to provide patients access to their records, as stipulated by the HIPAA Security Rule and Privacy Rule.
Are all health insurance companies covered by HIPAA
Yes, HIPAA applies to nearly all health insurance plans, including health maintenance organizations (HMOs), company group health insurance requirements, and government programs. The law defines these insurers as "health plans" and subjects them to the same standards for protecting patient information as healthcare clearinghouses and providers.
About Anna Voznaya